


The European Union Medical Device Regulation (MDR), In Vitro Diagnostic Regulation (IVDR) and new guidance around cybersecurity and AI measures are just a few of the many new regulatory burdens MedTech companies are having to bear. A staggering 67% of HealthTech professionals expect delays to innovation due to the need to meet regulations, while a further 90% have seen their regulatory costs increase over the last 12 months.
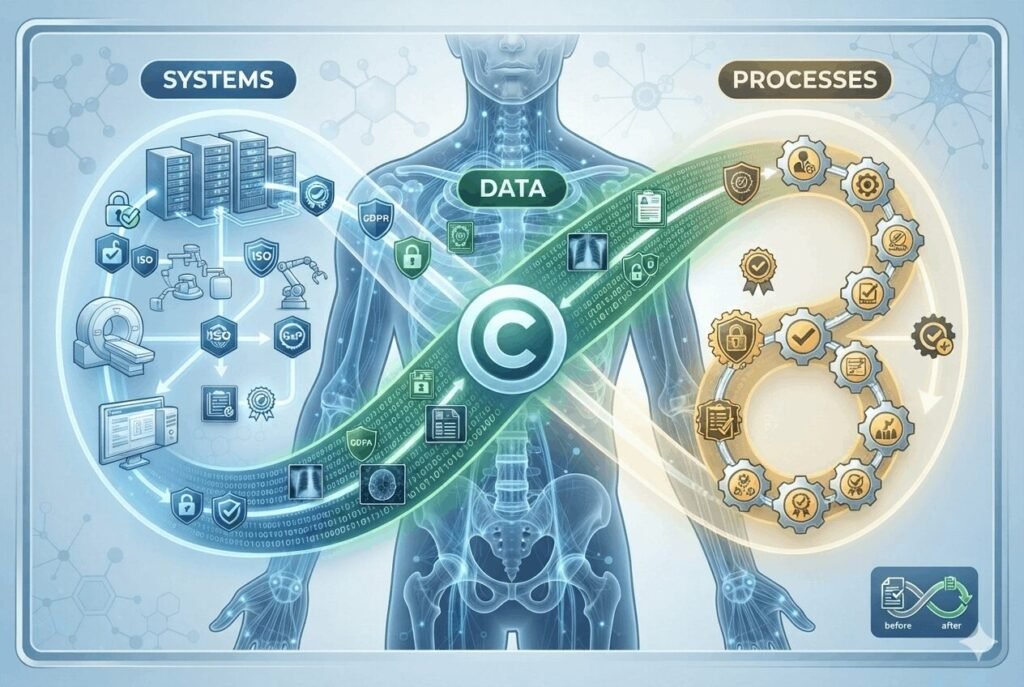
Tarn Brown, Life Sciences Industry Lead at Columbus, strongly believes that the real barrier is not regulation itself, but the inability to operationalise compliance consistently across systems, processes, people and data. To address this sticking point, she explains three keyways MedTech organisations can make the shift from episodic to embedded compliance, and turn an industry requirement into a competitive advantage.
It was only earlier this year that the Medicines and Healthcare products Regulatory Agency (MHRA) announced the biggest overhaul of clinical trial regulations in 20 years in the UK. While the MHRA’s clinical trial reforms are only one part of a broader regulatory picture, they reflect a wider direction of travel: regulators are expecting greater transparency, stronger governance and more consistent oversight across the life sciences ecosystem. As these regulatory expectations evolve, many MedTech organisations are beginning to realise that their existing manual approaches to compliance are being stretched beyond their limits.
Approaches that once worked in a more stable regulatory environment are now struggling to keep pace with the scale, speed and interconnected nature of today’s requirements. In many cases, this fragmentation is rooted in legacy infrastructure. Older, on-premise or poorly governed systems were not designed to support the level of integration required for modern regulatory expectations.
In response, many MedTech organisations are realising they need to rethink compliance at a structural level. Rather than attempting to optimise fragmented, document-heavy processes, they need to move towards a digital model in which compliance is embedded directly into systems, workflows and data.
There are three clear steps for MedTech companies to take on the journey. The pay-off? Continuous assurance, data-driven oversight, security and compliance by design. But above all, they will build a business foundation to accelerate market access to drive innovation with greater confidence, agility and control.
-
Say goodbye to disconnected systems
The burden of regulatory compliance is often magnified by siloed systems and inconsistent data practices. Only 36% of MedTech organisations have employed a unified data platform with comprehensive data management capabilities. Yet without such an approach, compliance becomes a reactive exercise rather than a strategic advantage, increasing exposure to delays, penalties and reputational risk. When quality, regulatory, manufacturing and post-market data sit in separate systems, organisations struggle to create a reliable audit trail, identify emerging risks quickly or demonstrate control during inspections.
So what’s holding many organisations back?
A common pain point is how to integrate modern platforms into pre-existing legacy environments without affecting validated processes. With the interoperability requirements of healthcare IT systems, almost 74% of MedTech companies struggle to make their data compliant. What’s more, under evolving regulatory pressures such as GDPR, data integrity and compliance have become even harder to uphold as systems and geographies expand.
-
Build a culture of compliance every day
MedTech companies must learn to unlock the potential of regulatory data to streamline compliance. Leading organisations are already achieving this by embedding digital solutions into their day-to-day activities. For instance, cloud-based platforms can provide real-time data access and support GxP compliance, while AI-driven monitoring tools can help ensure continuous quality assurance. The result? A digital compliance approach that allows companies to predict demand, optimise resources and maintain regulatory alignment.
This data integration across R&D, manufacturing or the supply chain is the backbone of digital transformation. However, while technology can provide the visibility and control, culture determines whether those controls are used consistently. Clear ownership, role-based training and leadership accountability are essential if compliance is to become part of everyday decision-making. Compliance must become part of the organisational DNA.
This starts with embedded compliance and data practices
Crucially, this transformation does not require a complete replacement of existing systems. Many organisations can achieve significant progress by prioritising transparent data governance and data ownership practices across the organisation. But this is easier said than done. Scaling digital initiatives is a major cultural challenge as it drives change across diverse teams and requires clear communication to overcome resistance. This is where organisational alignment is critical.
Cybersecurity, for instance, can no longer be an afterthought when the price risks patient safety, damaged reputations and legal consequences. In 2025 alone, there were 293 ransomware attacks on clinics, hospitals and healthcare tech providers – and the risk is only rising. Innovation must be secure by design, with robust access controls, encryption and governance frameworks embedded from the start. In this way, cybersecurity evolves into a ‘living’ capability, with continuous monitoring and structured patching processes ensuring that security is maintained over time, in line with regulatory expectations.
-
Dismantle barriers to innovation – where human oversight meets compliance by design
As compliance starts to move away from checklist-driven validation and towards more intelligent, risk-based approaches, it’s up to MedTech companies to ensure strategies enable innovation rather than become a barrier to it. Validation now needs to be guided by critical thinking, a true understanding of risk and practical approaches that leverage strong IT practices.
Digital compliance does not eliminate the need for human-in-the-loop approaches, particularly in areas such as AI and automated decision-making, but these alone may not satisfy regulators.
As dynamic AI models bring increased complexity due to their probabilistic outcomes, MedTech companies need to design AI systems with clear justification, traceability and validation in mind from the outset, rather than retrofitting for compliance later. Technologies such as AI-assisted validation, automated monitoring and continuous feedback loops are already enabling this shift, ensuring systems remain in a constant state of compliance.
Get ready for the digital era of compliance
Over the next five years, compliance will be defined by stronger governance of data, more rigorous lifecycle management and greater accountability at every stage of the product journey. Traditional models can’t keep up.
Organisations that move from episodic to embedded compliance will strengthen their market position for years to come. But it’s important to remember that the transition towards digital compliance requires more than just new technologies. It involves establishing the operational foundations, governance and ways of working needed to support continuous change.
A strong culture of compliance is essential to place MedTech organisations in a position to respond to regulatory change, accelerate innovation and maintain control over quality and safety.
For MedTech organisations, the next era of compliance will not be defined by more documentation, but by better control. Those with embedded compliance in their systems, data, processes and culture will be better placed to respond to regulatory change, protect quality and safety, and bring innovation to the market with greater confidence.